Scrutas
A forensic web audit platform, architected around a two-stage authorization model that earns trust before asking for access, then turns findings into a legally defensible, engineer-ready audit.
Built and running internally, 23 audit modules live. A forensic web audit platform whose hard problem was legal, not technical: a two-stage authorization model that shows real findings before asking for access, then turns a risky idea (auditing a site you don't own) into a defensible one.
The problem
Four risk domains, no single tool covers all of them
Enterprise e-commerce and SaaS platforms carry measurable risk across four domains simultaneously: revenue suppression, regulatory exposure (GDPR, PIPEDA, Quebec Law 25), security vulnerabilities, and accessibility liability. Existing tools each cover a slice.
Discovery
Two buyers, one authorization problem
E-commerce / SaaS ops · Primary
CAD $50M–$500M GMV, in-house engineering, no dedicated security audit capacity. Needs findings in dollars and regulation, not just severity labels.
Agencies & consultancies · Secondary
Deliver technical audits to clients; need a platform to underpin findings with defensible, structured data.
Backlog
User stories behind the architecture
Requirements
Spec'd as testable acceptance criteria
My role
Resolving the authorization tension before writing a spec
Security audit products face a structural bind: customers need to see value before committing, but running a full audit without authorization creates legal exposure for both sides. I designed the two-stage model that resolves it, modeled on patterns operators already trust (Google Search Console, Let's Encrypt ACME), then specified the full module coverage, competitive positioning, and pricing anchor strategy end to end.
The architecture
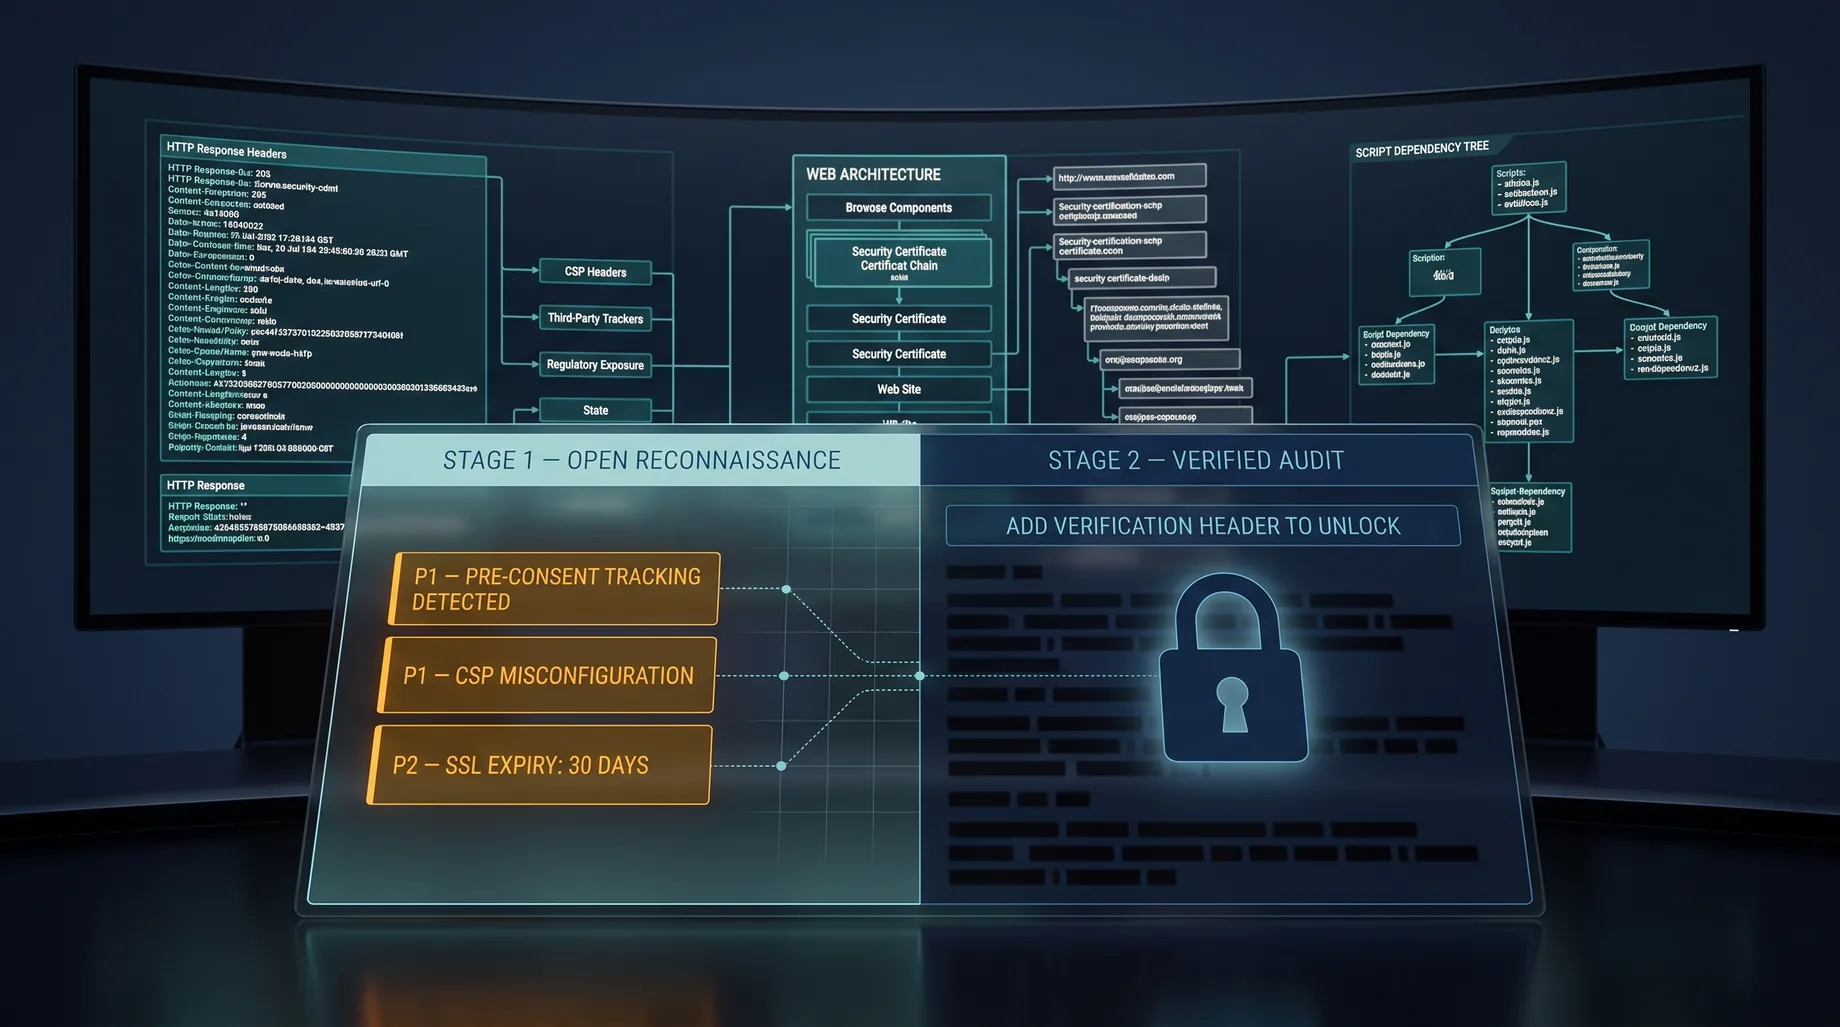
Lead with unauthenticated value. Convert with verified depth.
Zero commitment, immediate value
Runs on public HTTP responses only: headers, CSP, SSL, script inventory, WCAG contrast. Delivers 3–5 high-impact findings in under 3 minutes, no account required.
Authorized, legally defensible, complete
Gated behind a cryptographic domain-verification header. All 23 modules run: authenticated flows, storage analysis, credential scanning, subdomain enumeration.
Under the hood
A header, not a login, becomes the audit trail
The customer adds one HTTP response header; the platform polls for it every 60 seconds and logs the detection as a timestamped, immutable authorization record, attachable to any regulatory filing or client deliverable.
add_header X-Scrutas-Verify "scr_abc123_[token]";
// token properties
format: scr_[domain-hash]_[random-256-bit-hex] · validity: 72h · reuse: single-use
Pricing strategy
Anchor the price against the penalty, not the competitor
Every Stage 2 report states the maximum statutory penalty exposure identified. For pre-consent tracking under Quebec Law 25, that figure runs to $25M CAD per violation category. Against that, a $299 audit isn't a hard sell; it's the obvious next step.
Outcome
Live internally, running the full 23-module audit
Scrutas is built and running internally: the two-stage authorization model, all 23 audit modules, and the verification protocol are live. That two-stage model was the hard problem to solve: it's what turns a legally risky idea (auditing a site you don't own) into a defensible, authorized audit.
Roadmap
Five phases to platform
MVP: full audit engine + verification flow. Then agency white-label and findings API.
Monthly Monitor subscription + regression tracking. Then CI/CD integration and enterprise frameworks (HIPAA, SOC 2, PCI-DSS).
Third-party auditor marketplace: Scrutas becomes the infrastructure layer, not just the audit tool.
More case studies
Want a discovery sprint or a prototype like this one for your product? Book a call.